- PRODUCTS
- Security Platform
- BioStar X | On-Prem Security
- BioStar Air | Cloud Security
- BioStar 2
- Access Control
- Access Control Units
- Biometric ReadersNEW
- RFID Readers
- Mobile Credential
- Peripherals
- Wireless Door Locks
- SOLUTIONS
- SUPPORT
- ABOUT
- device_hubHUB


Zero Trust starts with identity. Not a credential.
A badge can prove possession. It cannot prove who is standing at the door.
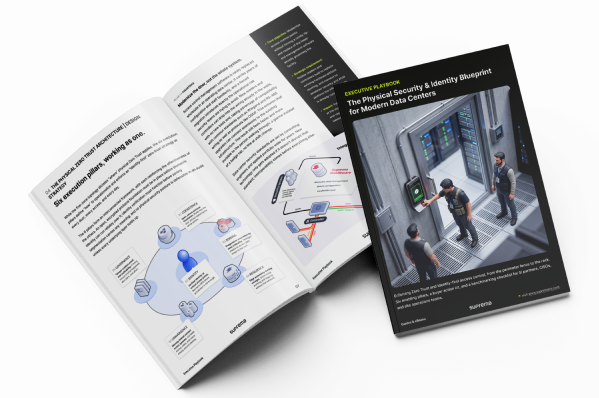
Discover how to build an identity-first physical Zero Trust architecture across the data center, from the perimeter to the rack.
Every door is a trust decision.
Data centers already segment physical access across increasingly sensitive zones. But segmentation alone isn't Zero Trust.
A credential can prove access rights. It does not always prove who is actually standing at the door. Cards can be shared or cloned. QR passes can be photographed and reused.
Identity-first security means tying every critical access event to a verified person, with the right level of assurance for each zone.
This playbook shows how to apply that principle through six execution pillars, supported by a vendor scorecard and facility benchmarking checklist.
Who is it for?
CISOs, Security Directors, Data Center Infrastructure leaders, Facilities teams, and system integrators designing or modernizing high-security environments.
Why download?
- Build identity-first access without unnecessary rip-and-replace
- Match authentication strength to the risk of each physical zone
- Keep access decisions running during network or server disruption
- Connect identity, access, video, and visitor evidence in one view
- Strengthen auditability with traceable access records
- Benchmark vendors and your current security architecture
Six pillars for putting physical Zero Trust into practice. Inside, discover how to:
01. Build on what you already have
Modernize access without unnecessary rip-and-replace.
02. Verify identity where assurance matters most
Move beyond credential possession with biometric and multi-factor authentication.
03. Increase assurance as risk increases
Apply stronger controls as access moves closer to critical compute.
04. Design for resilience
Keep authentication and access decisions operating through network disruption.
05. Connect your security signals
Bring identity, access, video, and visitor activity into a more complete operational picture.
06. Turn every access event into proof
Build the audit trail needed to answer who accessed what, when, and under which permissions.

